

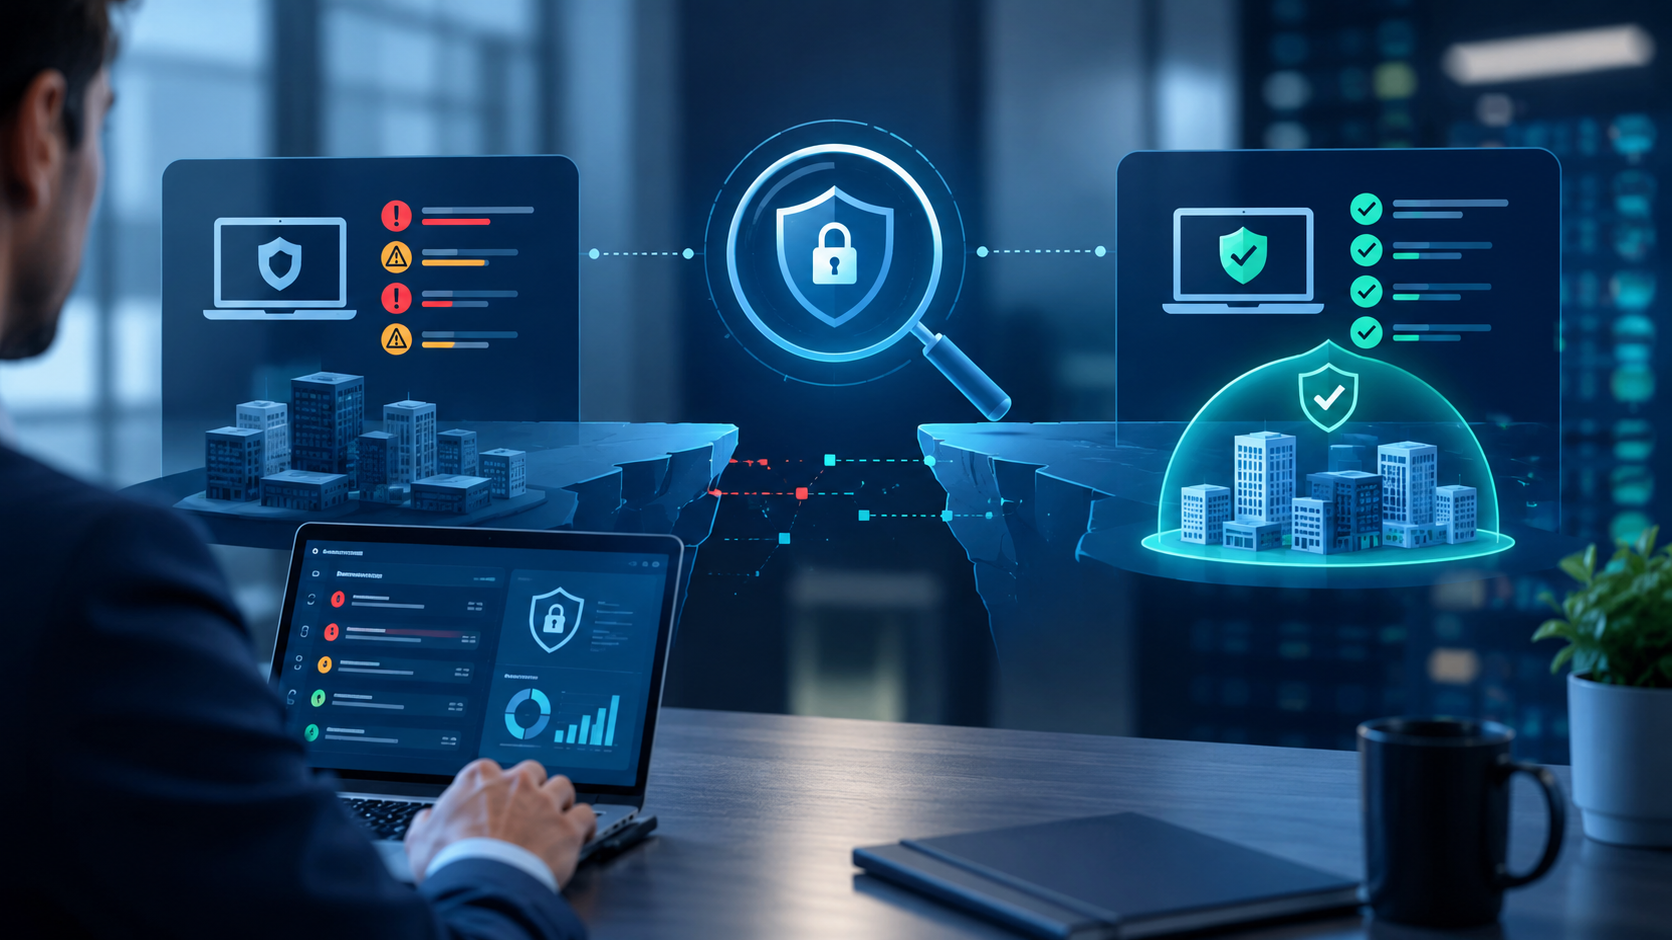

A cybersecurity gap analysis is a structured assessment that compares an organisation’s current security controls, processes, technologies, and practices against a defined security framework, regulatory requirement, or target security posture. It helps identify where existing protections fall short and what needs to be improved.
For organisations adopting cloud services, expanding through digital initiatives, or facing growing regulatory requirements, a cybersecurity gap analysis provides a practical way to understand security weaknesses before they become costly incidents.
What Is a Cybersecurity Gap Analysis?
A cybersecurity gap analysis evaluates the difference between where your organisation’s cybersecurity currently stands and where it needs to be.
The assessment typically compares existing security capabilities against requirements from frameworks and standards such as:
- ISO/IEC 27001
- NIST Cybersecurity Framework
- CIS Controls
- SOC 2 requirements
- GDPR security requirements
- NIS2 obligations
- DORA requirements for applicable financial entities
- Industry-specific security requirements
The goal is not simply to find vulnerabilities. A gap analysis looks more broadly at whether the organisation has the right people, processes, technologies, policies, controls, monitoring, and governance in place.
Cybersecurity Gap Analysis at a Glance
| Area | What Is Evaluated? |
| Security policies | Policies, procedures, ownership, and review cycles |
| Identity & access | Authentication, authorisation, privileged access, MFA |
| Network security | Segmentation, firewalls, remote access, network controls |
| Endpoint security | Device protection, patching, EDR/XDR capabilities |
| Cloud security | Cloud configurations, identities, workloads, data protection |
| Data security | Classification, encryption, retention, backup, access |
| Incident response | Detection, escalation, response, and recovery processes |
| Compliance | Alignment with applicable regulations and standards |
| Security awareness | Employee training and security responsibilities |
| Governance | Risk ownership, reporting, measurement, and accountability |
Why Is a Cybersecurity Gap Analysis Important?
Cybersecurity maturity does not automatically increase as an organisation adds more security tools.
An organisation may have firewalls, endpoint protection, cloud security platforms, vulnerability scanners, and security policies while still having significant gaps between its actual security posture and its target requirements.
For example, an organisation may discover that:
- Privileged accounts are not consistently protected with MFA.
- Critical systems are not covered by a formal vulnerability management process.
- Cloud resources have inconsistent security configurations.
- Security logs are collected but not monitored effectively.
- Incident response procedures have not been tested.
- Former employee accounts remain active.
- Backup recovery procedures have not been validated.
- Security responsibilities are unclear across internal and third-party teams.
A gap analysis brings these issues into a structured view so security leaders can prioritize remediation based on risk and business requirements.
How Does a Cybersecurity Gap Analysis Work?
A typical cybersecurity gap analysis follows several stages.
- Define the Assessment Scope
The first step is to establish what will be assessed.
The scope may include:
- Corporate IT infrastructure
- Cloud environments
- Applications and APIs
- End-user devices
- Data and databases
- Identity and access management
- Third-party systems
- Security operations
- Business-critical processes
The assessment scope should also identify the applicable regulations, standards, contractual requirements, and business objectives.
- Establish the Target Security State
The next step is determining what the organisation should meet.
This could be an established framework such as ISO 27001 or NIST CSF, a regulatory requirement such as NIS2, or an internally defined cybersecurity maturity target.
Without a defined target state, it is difficult to determine whether a particular security capability represents a meaningful gap.
- Assess the Current Security Posture
Security professionals review the organisation’s existing controls and practices.
Depending on the scope, this can involve:
- Documentation reviews
- Stakeholder interviews
- Technical assessments
- Configuration reviews
- Access reviews
- Vulnerability information
- Security architecture analysis
- Cloud configuration assessments
- Incident response reviews
- Evidence collection
This stage establishes the organisation’s current security baseline.
- Identify and Classify Gaps
The current state is then compared with the target state.
Gaps can be classified according to factors such as:
- Business impact
- Security risk
- Regulatory importance
- Exploitability
- Asset criticality
- Implementation complexity
This helps distinguish urgent security issues from lower-priority improvements.
- Build a Remediation Roadmap
The final output should be more than a list of security problems.
A useful gap analysis produces a prioritised roadmap showing:
Gap → Risk → Recommended action → Priority → Owner → Target timeline
For example:
Gap: Privileged accounts lack consistent MFA
Risk: Increased risk of unauthorized administrative access
Action: Implement phishing-resistant MFA for privileged identities
Priority: High
Owner: IT/Security team
This turns the assessment into an actionable security improvement plan.
What Is Included in a Cybersecurity Gap Analysis?
The exact scope depends on the organisation, but a comprehensive assessment commonly covers the following areas.
- Governance and Security Policies
This examines whether cybersecurity policies exist, whether responsibilities are clearly assigned, and whether policies are reviewed and updated.
- Identity and Access Management
The assessment looks at authentication, authorisation, privileged access, MFA, account lifecycle management, and access reviews.
- Vulnerability and Patch Management
Security teams assess whether vulnerabilities are identified, prioritised, remediated, and tracked within defined timelines.
- Network and Infrastructure Security
This can include network segmentation, firewall controls, remote access, infrastructure hardening, and monitoring.
- Cloud Security
As organisations increasingly depend on cloud services, cloud security becomes an important part of the assessment.
The review may examine identity permissions, storage configurations, workload security, encryption, logging, network controls, secrets management, and cloud governance.
- Application and Data Security
Applications, APIs, databases, and sensitive information may be assessed for appropriate access controls, encryption, secure development practices, and data protection measures.
- Security Monitoring and Incident Response
The assessment examines whether security events can be detected and whether the organisation has defined procedures for investigation, containment, communication, recovery, and post-incident improvement.
- Business Continuity and Recovery
Critical systems, backups, disaster recovery processes, recovery objectives, and restoration procedures may also be reviewed.
When Do You Need a Cybersecurity Gap Analysis?
There is no single trigger that applies to every organisation. However, several situations make a gap analysis particularly valuable.
- Before a Major Digital Transformation
Major technology changes can introduce new attack surfaces and security dependencies.
If your organisation is undertaking digital transformation services, migrating applications, modernising infrastructure, adopting SaaS platforms, or implementing new digital workflows, a gap analysis can establish security requirements before new systems become deeply embedded.
Cybersecurity should be considered as part of transformation planning rather than added after implementation.
- During Cloud Migration or Cloud Expansion
Moving workloads to the cloud changes how organisations manage identities, networks, data, workloads, and access.
A cybersecurity gap analysis can help identify weaknesses before or during cloud migration and can complement cloud services such as cloud architecture, migration, security, and managed operations.
- Before a Compliance or Certification Initiative
Organisations preparing for ISO 27001 certification or responding to regulatory requirements may use a gap analysis to understand their current level of alignment.
It can help identify missing controls and documentation before a formal audit or compliance assessment.
- After a Security Incident
A breach or significant security event can expose weaknesses that were previously unknown.
A post-incident gap analysis can examine broader security controls and determine whether similar weaknesses exist elsewhere in the environment.
- When the IT Environment Has Changed Significantly
Mergers, acquisitions, new offices, remote-work expansion, new applications, cloud adoption, and infrastructure modernisation can all change an organisation’s risk profile.
A gap analysis provides an opportunity to reassess security controls against the new environment.
- When Security Spending Needs Better Prioritization
Security teams often face competing demands and limited resources.
Instead of implementing controls based only on technology trends or isolated findings, a gap analysis can help create a prioritized improvement roadmap aligned with business risks.
Cybersecurity Gap Analysis vs. Vulnerability Assessment
These terms are sometimes used interchangeably, but they address different questions.
| Cybersecurity Gap Analysis | Vulnerability Assessment |
| Evaluates overall security posture | Identifies technical vulnerabilities |
| Reviews people, processes, and technology | Primarily focuses on systems and technical weaknesses |
| Compares current state with a target state | Identifies known security weaknesses |
| Can assess compliance and governance | Usually focuses on technical exposure |
| Produces a broader remediation roadmap | Produces vulnerability findings and remediation priorities |
A vulnerability assessment can therefore be one input into a broader cybersecurity gap analysis.
Cybersecurity Gap Analysis vs. Cybersecurity Risk Assessment
A risk assessment focuses on identifying and evaluating risks to business assets, systems, processes, and information.
A gap analysis focuses on the difference between the current security posture and a defined target state.
The two activities can work together:
Risk assessment → Understand risks → Gap analysis → Identify control deficiencies → Remediation roadmap
Organisations may use both when developing a broader cybersecurity improvement program.
What Are the Benefits of a Cybersecurity Gap Analysis?
A properly scoped assessment can help organisations:
- Identify Security Weaknesses
It provides a structured view of missing, inconsistent, or ineffective controls.
- Prioritise Remediation
Not every gap requires the same urgency. A risk-based approach helps teams focus resources on areas with greater business or security impact.
- Improve Regulatory Readiness
Organisations can identify potential control and documentation gaps before formal audits or regulatory reviews.
- Support Technology Decisions
The findings can help security and IT teams determine where additional technologies, process changes, or specialist expertise may be required.
- Improve Security Governance
A documented baseline and roadmap give leadership greater visibility into cybersecurity priorities, ownership, and progress.
- Support Business Transformation
When security requirements are considered alongside digital transformation services, cloud adoption, application modernisation, and other technology initiatives, security becomes part of the transformation lifecycle rather than a separate activity.
How Often Should You Conduct a Cybersecurity Gap Analysis?
There is no universal annual schedule that applies to every organisation.
The frequency should reflect the organisation’s risk profile, regulatory obligations, technology changes, and security maturity.
A new assessment may be appropriate after:
- Major cloud migration
- Significant infrastructure changes
- Mergers or acquisitions
- Major application launches
- New regulatory requirements
- Significant security incidents
- Changes to business-critical systems
- Major changes in third-party relationships
Organisations with rapidly changing environments may also perform periodic reassessments to measure progress against their cybersecurity roadmap.
What Should a Cybersecurity Gap Analysis Report Include?
A useful final report should make the findings understandable to both technical teams and business leadership.
It can include:
- Executive summary – Key findings and business implications.
- Assessment scope – Systems, processes, locations, and standards reviewed.
- Current-state assessment – Existing security capabilities.
- Gap register – Identified control and process gaps.
- Risk classification – Relative priority of identified gaps.
- Target state – Expected security controls or maturity.
- Remediation recommendations – Actions required to address gaps.
- Implementation roadmap – Short-, medium-, and long-term actions.
- Ownership – Teams or stakeholders responsible for remediation.
- Measurement approach – How progress will be monitored.
When Should You Hire Cybersecurity Experts for a Gap Analysis?
Internal IT teams can often provide valuable information about existing infrastructure and controls. However, complex environments may require specialized cybersecurity expertise.
You may consider Hire cybersecurity experts when:
- Your environment spans multiple cloud platforms.
- You operate across multiple regulatory jurisdictions.
- You are preparing for ISO 27001 or another formal security framework.
- You have limited internal cybersecurity resources.
- Your infrastructure includes legacy and modern systems.
- You need an independent assessment.
- You are responding to significant security findings or an incident.
- You need a structured roadmap remediation.
Working with external specialists can also provide an independent perspective that complements internal security teams.
How Sphinx Can Help with Cybersecurity Gap Analysis
Sphinx Worldbiz helps organisations assess and improve their cybersecurity posture across infrastructure, applications, cloud environments, data, and security processes.
Our cybersecurity services can support organisations with security assessments, compliance readiness, vulnerability management, cloud security, security operations, and cybersecurity improvement initiatives.
For organisations expanding their cloud services, modernising technology, or implementing digital transformation services, cybersecurity requirements can be incorporated into the transformation roadmap rather than addressed as a separate activity.
Where specialised expertise is required, organisations can also Hire cybersecurity experts to support security assessments, implementation, monitoring, and remediation initiatives.
The objective is to move from a fragmented view of security gaps to a prioritised roadmap that teams can implement and measure.
Frequently Asked Questions
What is a cybersecurity gap analysis?
A cybersecurity gap analysis compares an organisation’s current security controls and capabilities with a defined target state, framework, standard, or regulatory requirement. It identifies gaps and helps create a prioritised remediation plan.
How long does a cybersecurity gap analysis take?
The duration depends on the organisation’s size, assessment scope, technology environment, number of locations, regulatory requirements, and availability of evidence. A focused assessment can be completed faster than an enterprise-wide review.
Is a cybersecurity gap analysis the same as a security audit?
No. A gap analysis primarily identifies differences between the current and desired security state. A formal audit typically evaluates whether specified requirements or controls are being met according to an established audit process.
Is vulnerability scanning enough to identify cybersecurity gaps?
No. Vulnerability scanning primarily identifies technical weaknesses. A gap analysis can additionally examine governance, policies, identity management, processes, security operations, compliance, people, and technology.
Can a gap analysis assess cloud security?
Yes. Cloud environments can be included in a gap analysis. The assessment may review identity and access controls, configurations, workloads, network security, logging, encryption, data protection, and cloud governance.
Should a gap analysis be performed before cloud migration?
It can be useful before migration because it helps identify existing security deficiencies and define security requirements for the target cloud environment. The assessment can also be repeated after migration to validate the new environment.
What frameworks can be used for a cybersecurity gap analysis?
Depending on the organisation’s objectives, an assessment may reference frameworks and standards such as ISO/IEC 27001, NIST CSF, CIS Controls, SOC 2, GDPR, NIS2, DORA, or industry-specific requirements.
Who should conduct a cybersecurity gap analysis?
It can be conducted by an internal security team, an external cybersecurity provider, or a combination of both. The appropriate approach depends on internal expertise, assessment of complexity, independence requirements, and the organisation’s security objectives.
Final Takeaway
A cybersecurity gap analysis answers a practical question:
“Where are we today, where do we need to be, and what should we do to close the difference?”
It is particularly useful when organisations undergo digital transformation, moving to the cloud, preparing for compliance requirements, responding to security incidents, or reassessing their security posture.
By identifying control gaps and converting them into a prioritized remediation roadmap, organisations can make cybersecurity improvements more structured, measurable, and aligned with business requirements.