

Your business may have cybersecurity policies in place. But are they enough to protect your organization from evolving cyber threats and NIS2 compliance risks? Across Europe, cybersecurity is no longer just an ...
Accurate forecasting is no longer just an operational requirement for renewable energy generators. It is becoming a key factor in revenue protection, market participation, and long-term asset profitability. Win...

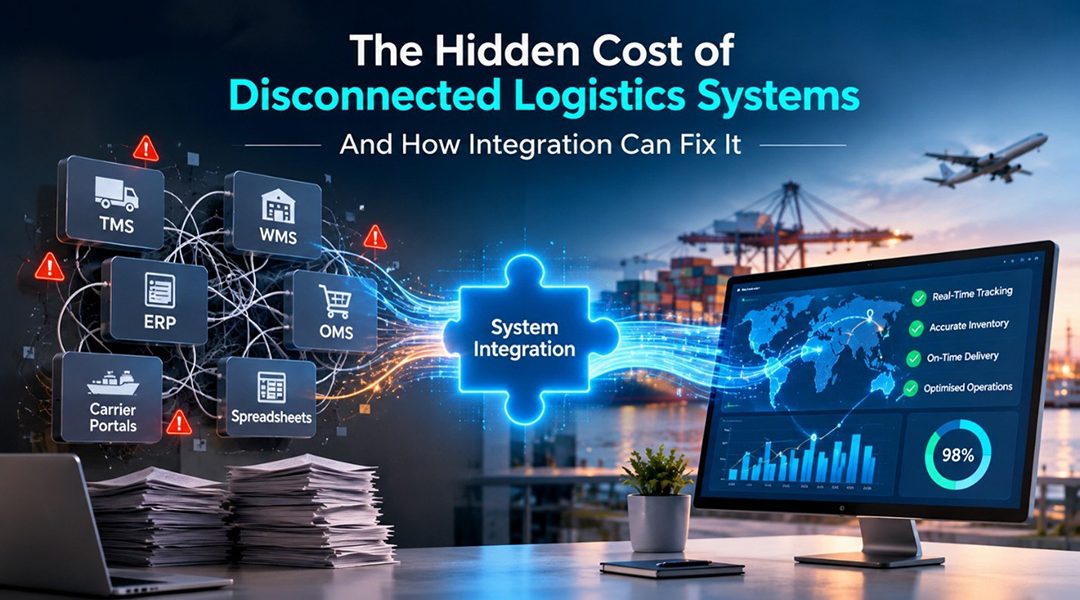
Logistics operations depend on multiple systems working together. Transportation management systems (TMS), warehouse management systems (WMS), enterprise resource planning (ERP), order management systems (OMS),...
Artificial intelligence is changing more than the technology enterprises use. It is reshaping how organizations organize work, make decisions, and what skills they need to remain competitive. As businesses move...
End-to-end shipment visibility helps logistics companies track goods across transport stages, identify potential delays, and provide reliable delivery updates. Yet many organizations still struggle to achieve i...
Digital transformation is not simply about adopting new technology. It is about connecting systems, securing data, improving business processes, and building the operational capabilities needed to scale change ...
Europe’s transition towards renewable energy is changing how electricity is generated, distributed, stored, and consumed. As wind and solar power account for a growing share of the energy mix, renewable e...
Banks across Europe are modernizing their technology infrastructure to improve operational efficiency, accelerate digital banking, and deliver better customer experiences. Cloud computing plays a central role i...
SaaS companies gather, handle, keep, analyze and share large volumes of personal information via applications, APIs, databases, analytics platforms and cloud infrastructure. That’s why data protection is ...

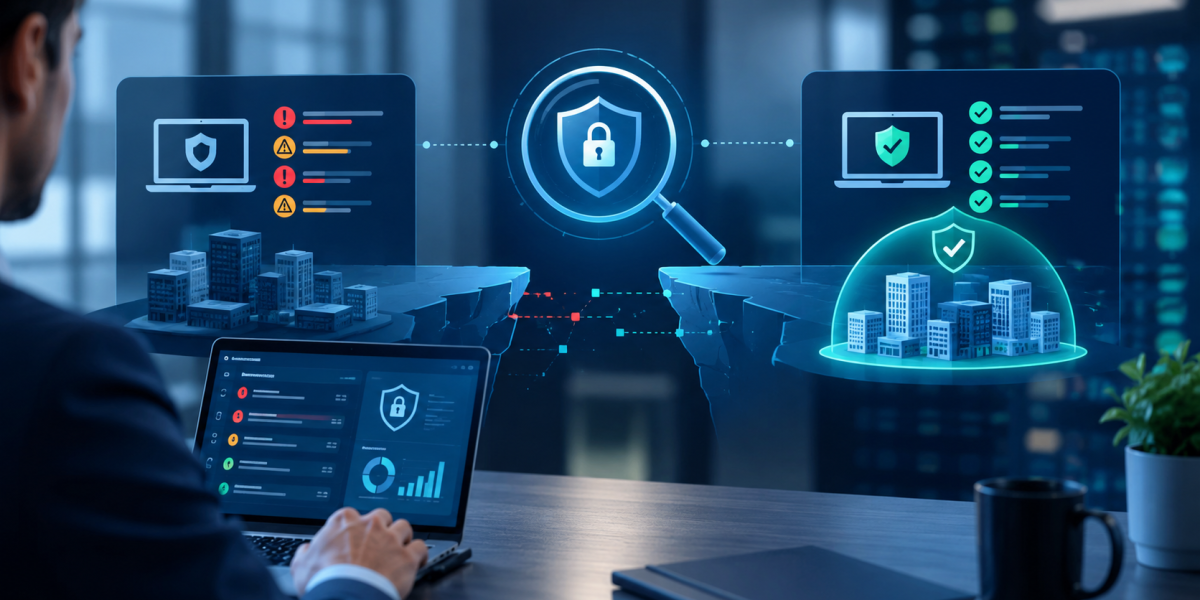
A cybersecurity gap analysis is a structured assessment that compares an organisation’s current security controls, processes, technologies, and practices against a defined security framework, regulatory require...